Audit Log
Purpose: Centralized, immutable record of administrative actions, authentication events, and security adjustments across the organization.
Investigate Security Incident
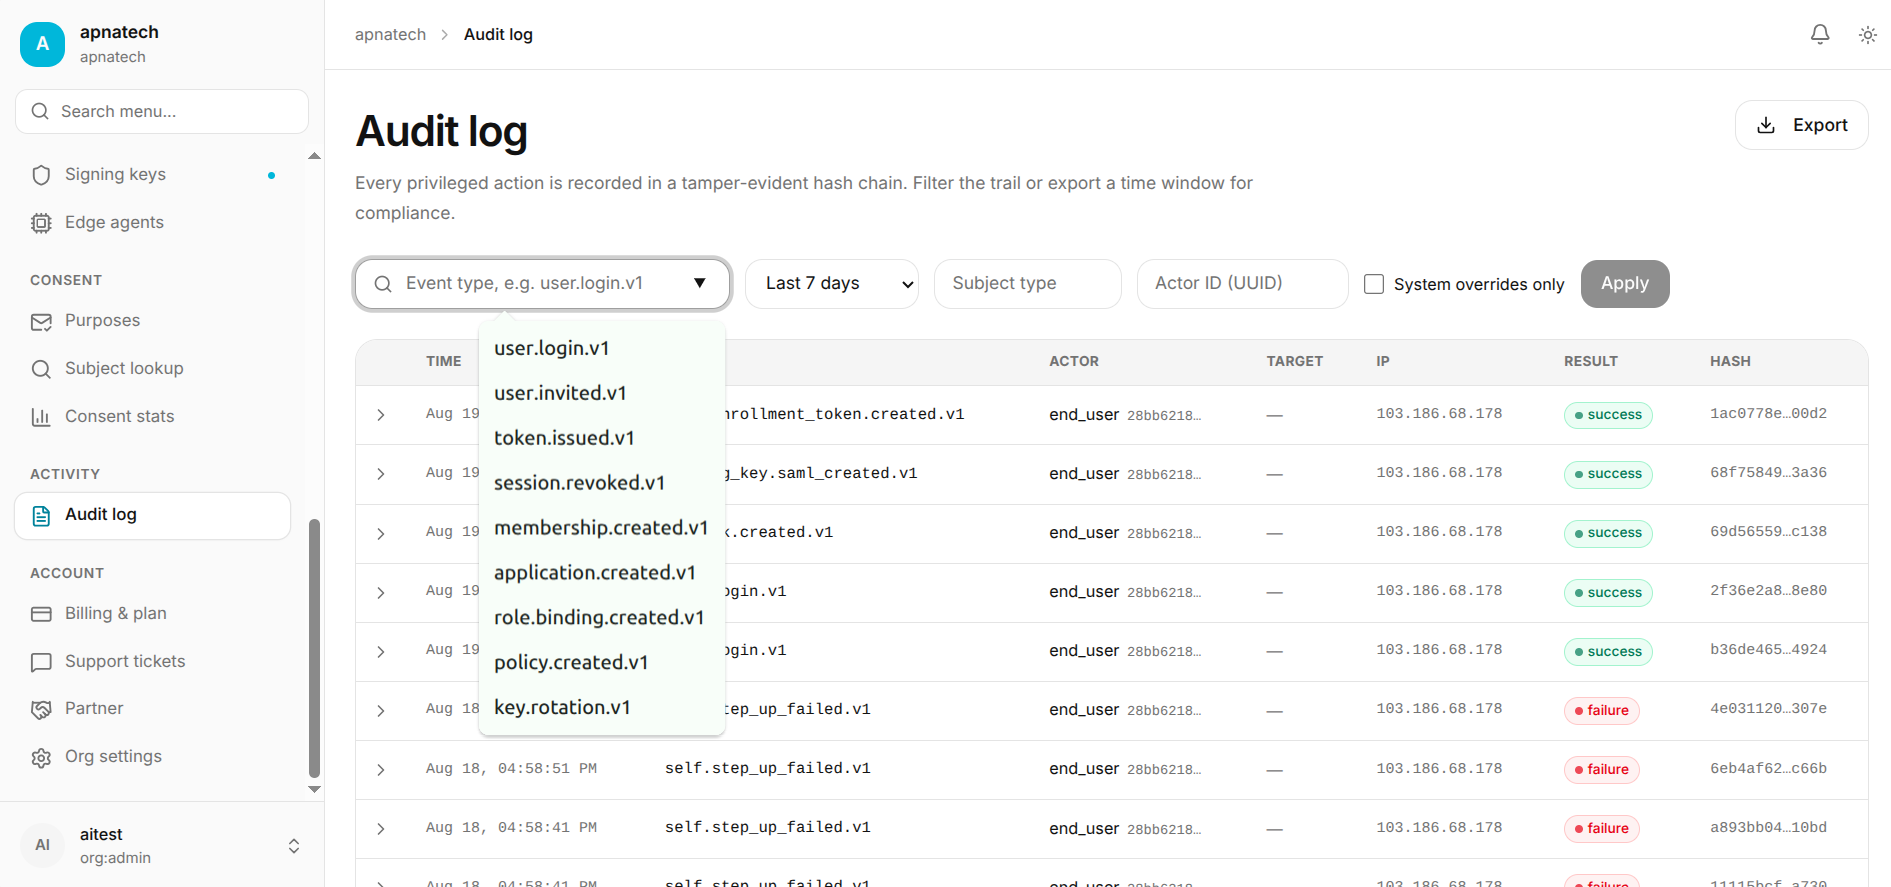
- Step 1: Filter by target user email or resource ID.
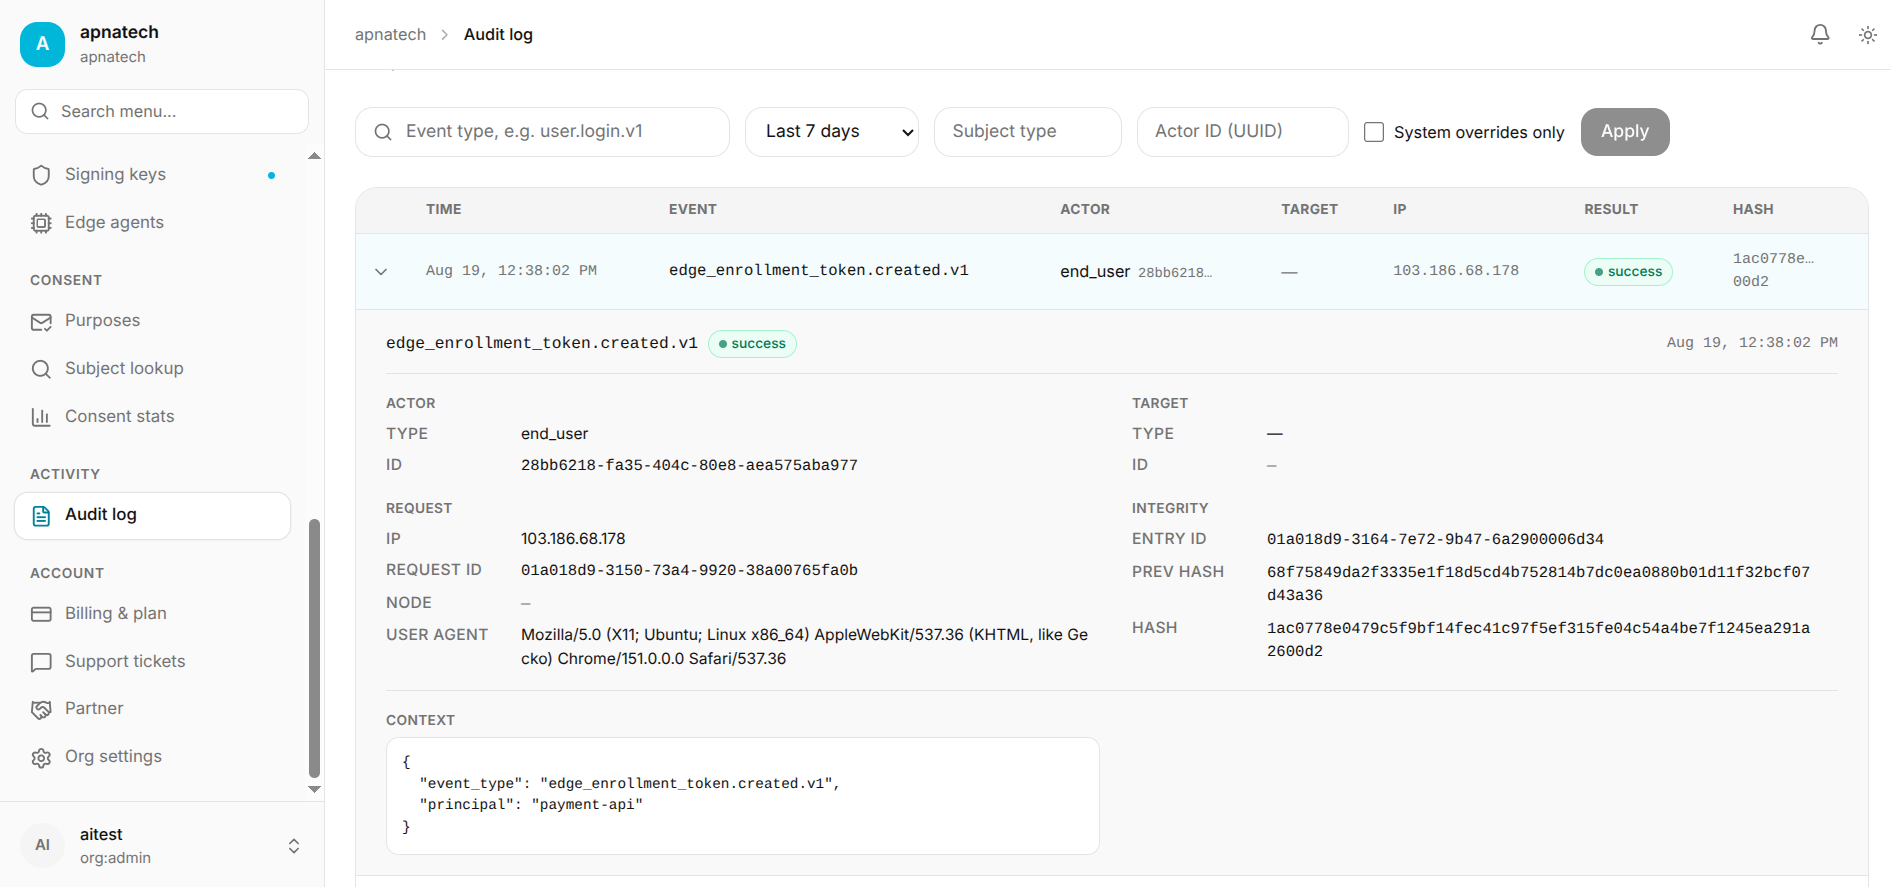
- Step 2: Inspect IP addresses and user agents for suspicious activity.
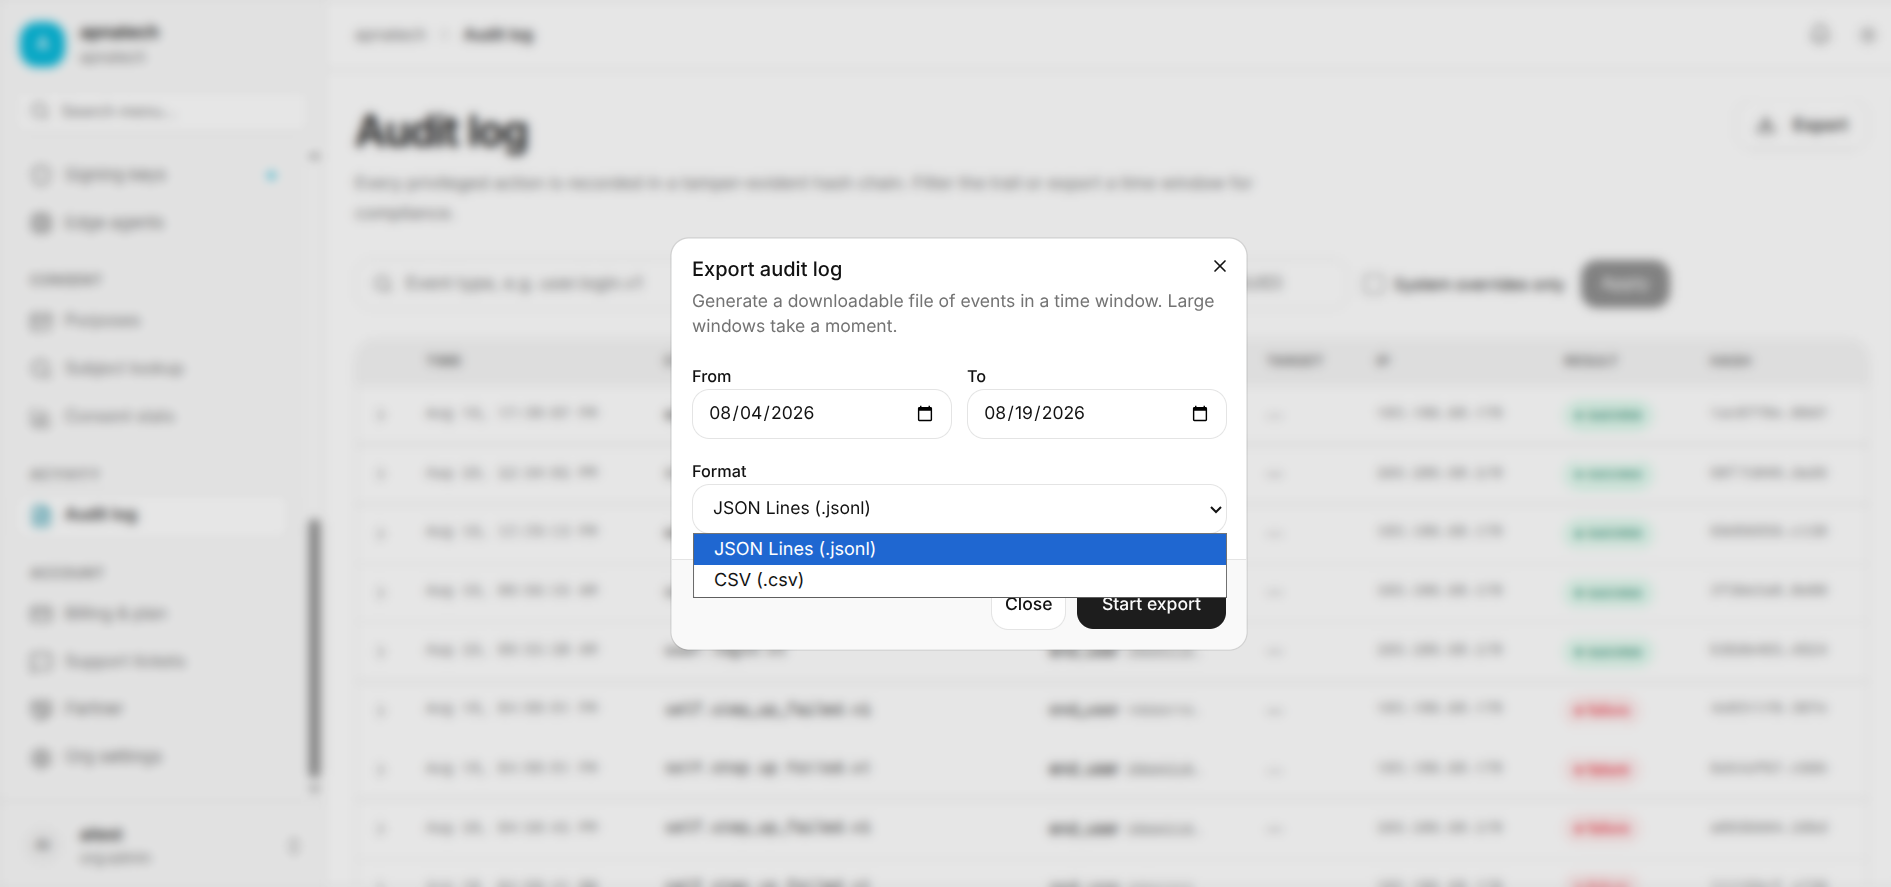
- Step 3: Export filtered log data for external SIEM analysis or forensic reporting.
Retention & Export
- Configure automated log forwarding via Webhooks or SIEM connectors.
- Retention policies govern historical log availability based on your plan (Billing & Plan).