API Keys
Purpose: Manage machine credentials for integrations, automation, and programmatic access.
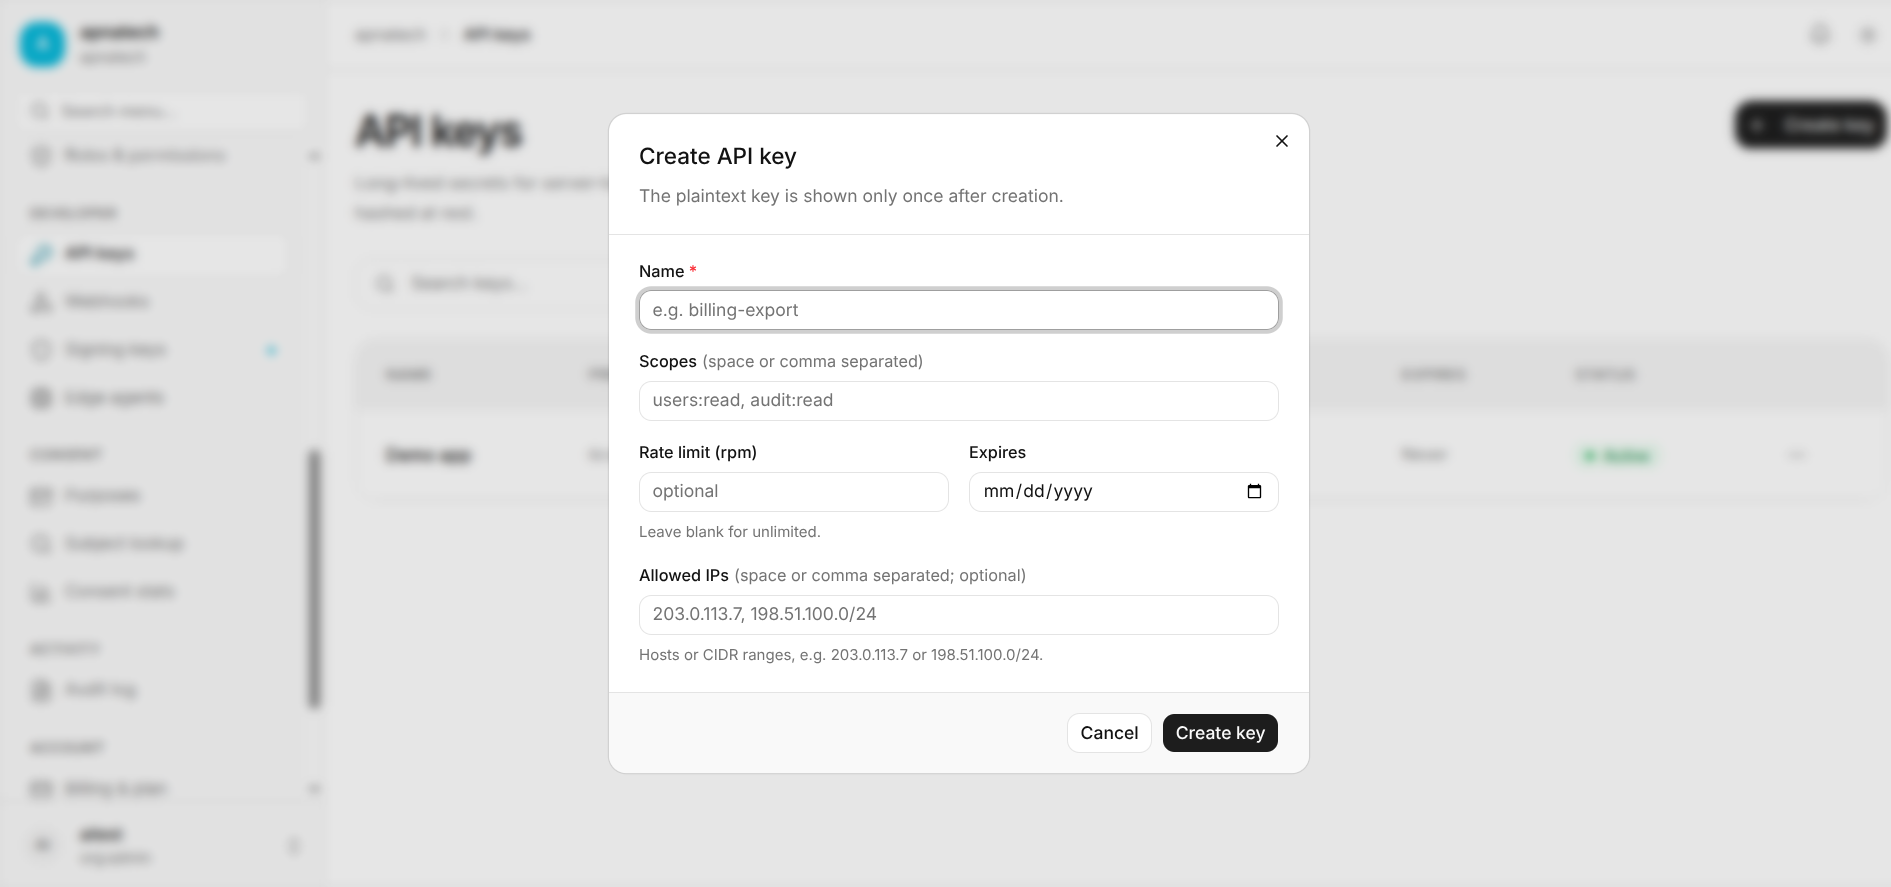
Create a Key
- Provide a descriptive name and owner.
- Select scopes that limit the key’s permissions (read-only vs. write).
- Optionally set an expiration (recommended for short-lived keys).
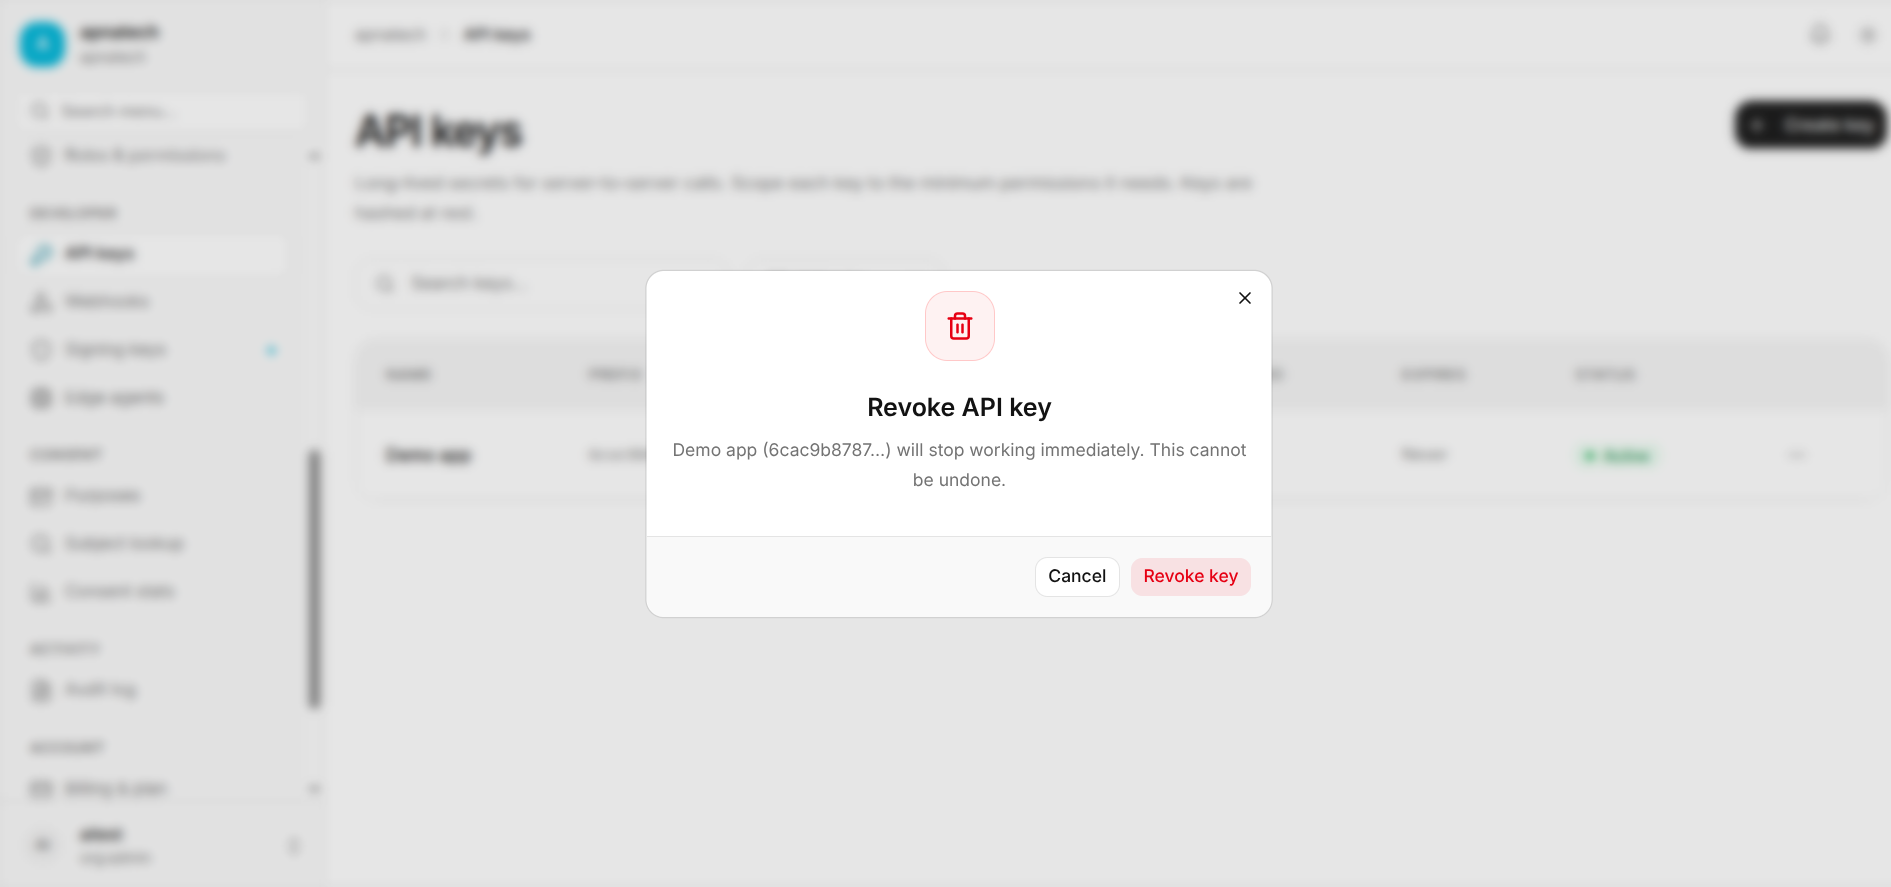
Revoke a Key
- Immediate action to block access from compromised or retired credentials.
Security & Best Practices
- Use narrow scopes and shortest practical lifetimes.
- Store secrets in secret management systems (vaults) and not in code or email.
- Audit and remove keys that are unused beyond a threshold (e.g., 90 days) via Audit Log.
Troubleshooting
- API requests returning unauthorized:
- Confirm key is active, not expired, and the scope covers the requested operation.
- Check for clock drift in signed token-based implementations.
Operational Checklist
- Enforce rotation schedule and require owners to validate downstream updates before revoking old keys.